Clean Risk and Governance Workbook
Nine editable Excel sheets connecting a 100-record risk register, 24 starter controls, treatment plan, evidence register and calculated executive dashboard.
Cyber risk decisions supported by evidence and accountable ownership
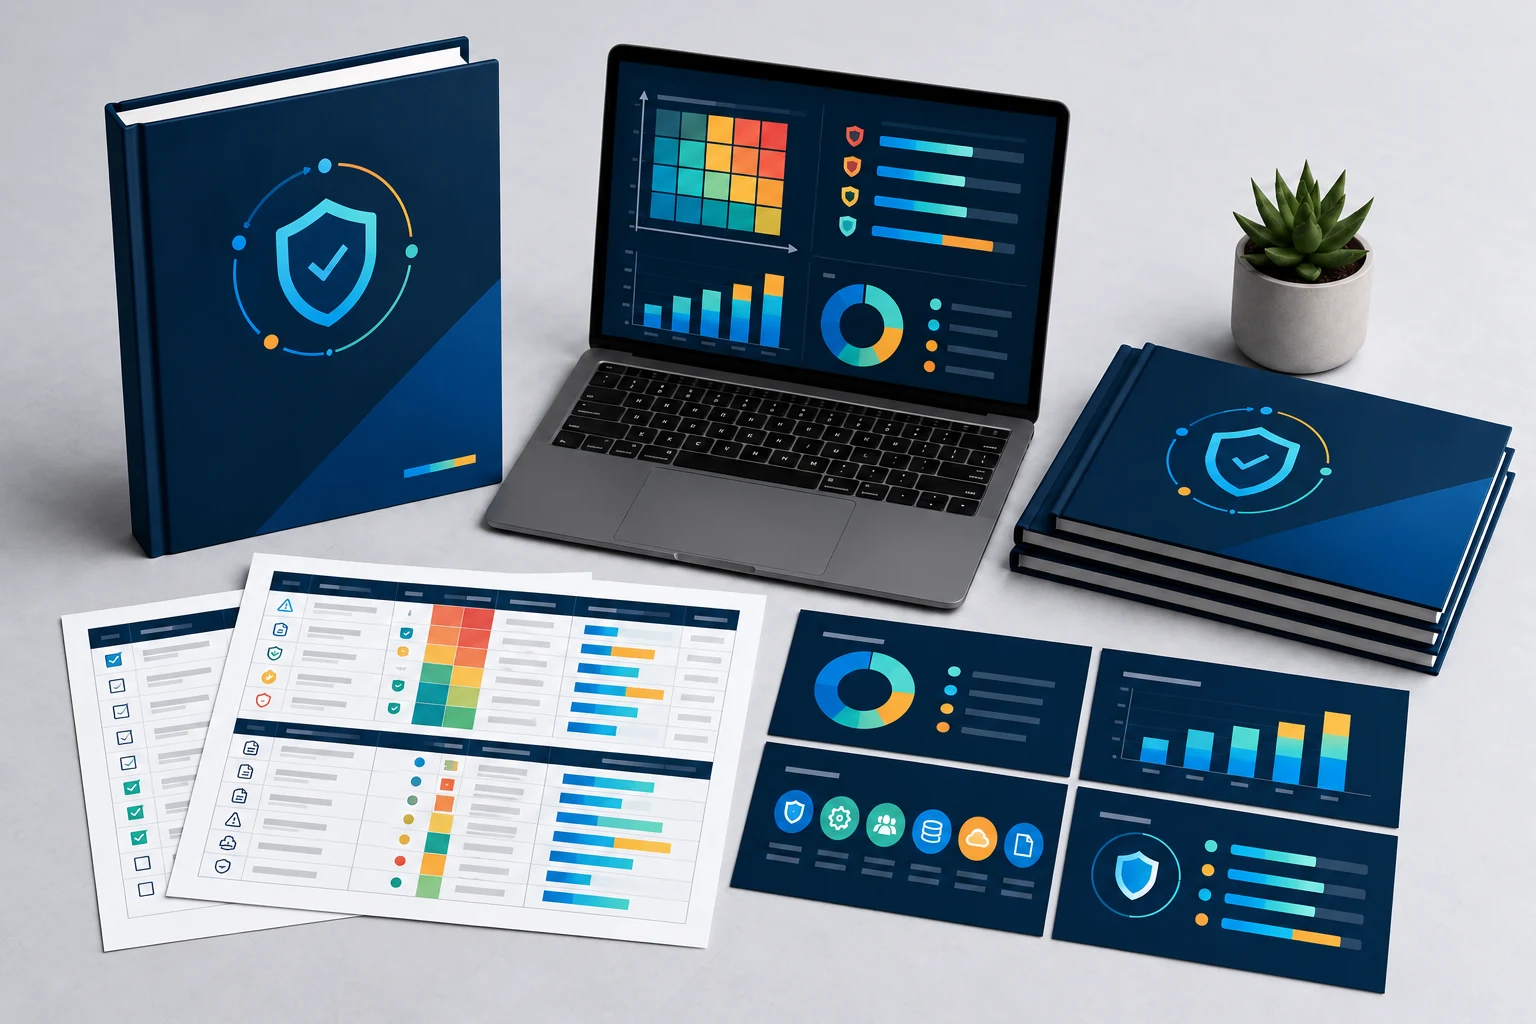
Connect cyber risk scenarios, control assessment, treatment actions and evidence with an executive dashboard. Includes clean and fictional worked-example Excel workbooks, a handbook, editable executive review and quick-start guide.
IT managers, security leads and governance teams
Connect risk evidence, assessment gaps, treatment owners and leadership decisions.
Nine editable Excel sheets connecting a 100-record risk register, 24 starter controls, treatment plan, evidence register and calculated executive dashboard.
Six risk scenarios, 24 starter controls and linked treatment and evidence examples illustrate incomplete assessment, expired acceptance and stale evidence.
Separate inherent and assessed residual likelihood-impact scores, configurable risk bands, local 0–4 control levels, target gaps and assessment coverage by function.
Accountable action owners, due dates, success measures, budget estimates, acceptance authority, management decisions and closure evidence.
A PDF handbook explains fields, scoring rules, review cadence and limitations. An editable nine-slide presentation supports recurring leadership reviews.
A quick-start PDF and README explain the clean/example workflow, package contents, internal-use terms and support.
Immediate digital access after successful payment.
Product overview
Collect risk scenarios and control evidence in editable registers. Assess current residual likelihood and impact separately from inherent risk, then use the dashboard to review bands, missing assessment and overdue treatment.
The toolkit uses the six NIST CSF functions for high-level grouping. Its starter controls and local 0–4 assessment scale are not a complete CSF mapping, official NIST maturity assessment or certification. Business owners retain responsibility for scope, evidence and risk acceptance.
Cybersecurity review areas
Each area supports a consistent working process while preserving the detail needed for ownership, review and action.
Review risk appetite, delegated authority, policy ownership and supplier security oversight.
Document critical services, assets, dependencies and risk scenarios with business consequences.
Assess access controls, data handling, secure configuration and staff awareness using evidence.
Review logging coverage, alert handling, detection tests and event analysis.
Assess incident authority, triage, communications, containment and evidence preservation.
Review restore tests, recovery priorities, communications and corrective actions.
Key benefits
Business outcomes
Who should use this
Designed for IT managers, security leads, CIOs, service owners, risk reviewers and governance teams coordinating a recurring cybersecurity review.
Why K2 DigiPro
Dashboard counts link to recorded risks, controls, treatment actions and evidence.
Editable criteria expose the risk bands and the local control assessment method.
Missing scores stay unassessed. Stale or incomplete evidence prevents a control from counting as assessed.
Record business consequences, acceptance authority, management rationale and verified closure.
Clean and example workbooks, handbook, presentation, quick start and README follow the K2 DigiPro toolkit standard.
A clearer cybersecurity review
Connect assessment records, treatment progress and leadership decisions in a repeatable review process.
Yes. The toolkit is designed as an adaptable starting point for your organisation, measures and review process.
No. The displayed price is a one-time purchase for this digital toolkit.
After successful payment, access is provided through your account using a verified download link.